Quick summary
- A practical architecture for AI agent authorization using policy enforcement, least privilege, risk-based approval, short-lived credentials, and auditable tool calls.
- AI agents can execute multi-step plans at machine speed. If authorization is checked only at sign-in, a bad instruction or abused tool can turn legitimate access into actions that exceed the user's intent.
- Inventory every agent tool, classify operations by impact, and place a mandatory policy enforcement point before any call that reads internal data or changes system state.
What happened
AI agent authorization answers a precise question: may this agent perform this action, with this tool, on this resource, at this moment? Authentication establishes identity. Authorization must evaluate purpose, scope, data sensitivity, session state, and the risk of every proposed tool call.
Why conventional application roles are insufficient
Conventional applications usually expose workflows designed in advance. An agent can select tools, create an action sequence, and adapt its plan from intermediate results. A broad permission such as “use email” or “access the database” does not define which mailbox, recipient, table, field, or number of records is permitted.
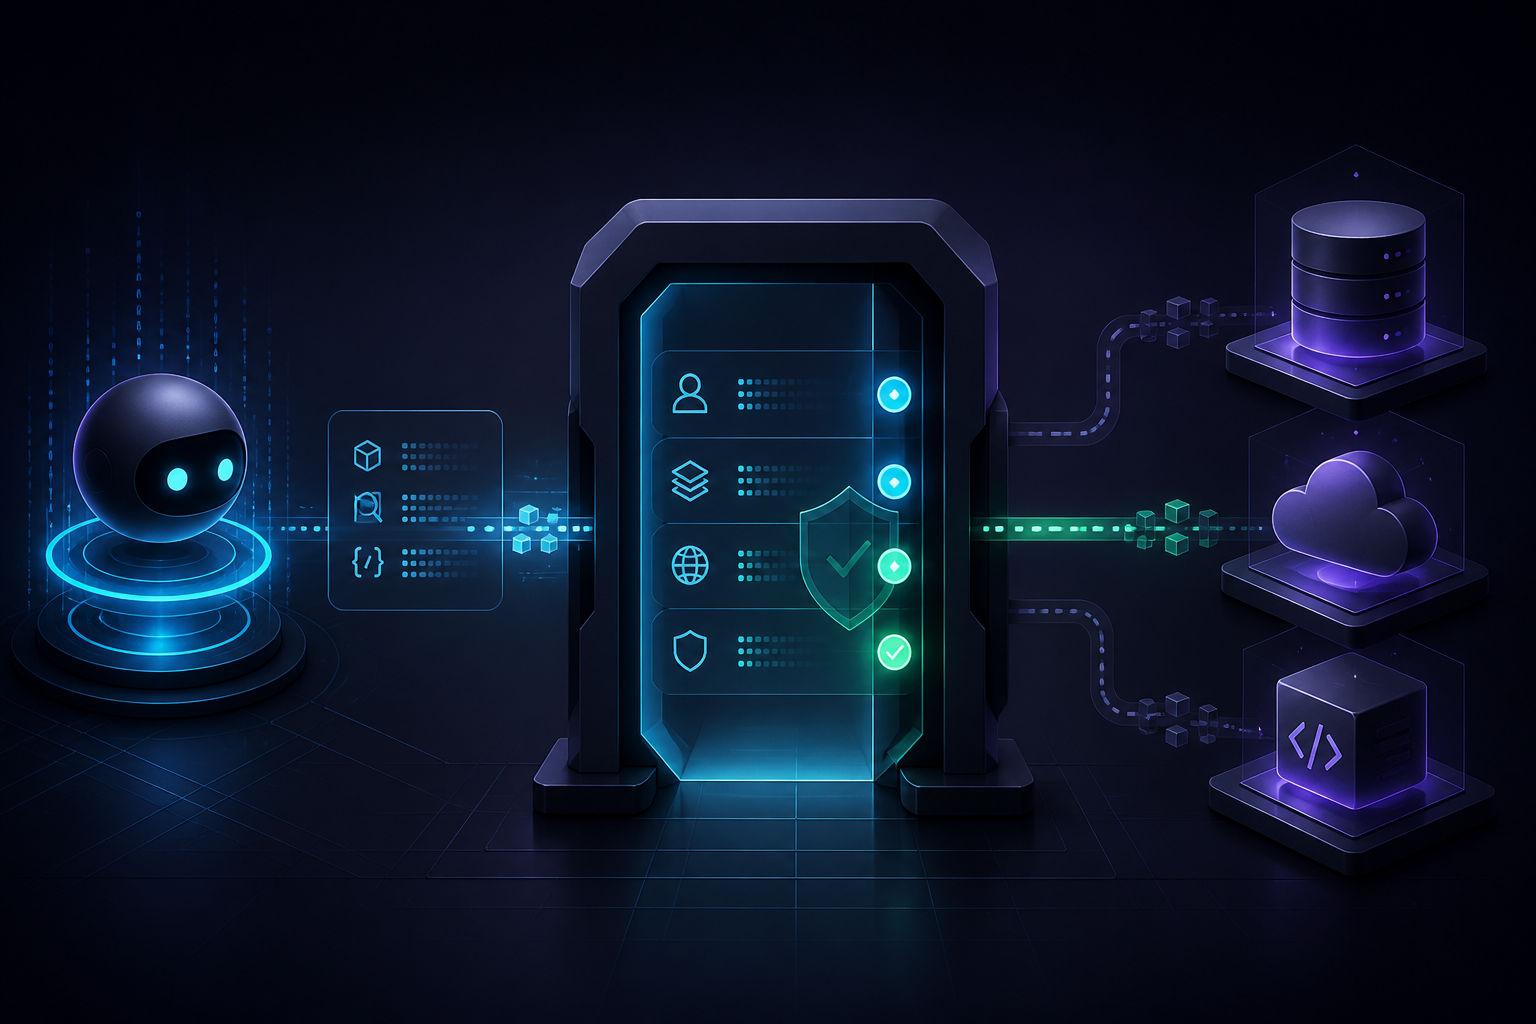
The authorization boundary belongs immediately before tool execution. The agent may propose an action, but a separate policy enforcement point must allow it, deny it, narrow its parameters, or require approval.
Four inputs to an authorization decision
- Principal: the user, service account, or workload delegating authority.
- Action: the exact operation, such as read, create, send, update, delete, or execute.
- Resource: the target tenant, project, repository, dataset, record set, or recipients.
- Context: session purpose, request origin, sensitivity, environment, time, and previous-step results.
An authorization architecture for agents
Each tool should publish its input schema, state-changing operations, and resource boundaries. Before execution, the agent sends a normalized authorization request to a policy decision point. The response can do more than allow or deny: it may cap record counts, remove sensitive fields, force read-only mode, or request human confirmation.
Credentials should never be placed directly in model context. A broker can retain credentials and issue a short-lived, narrowly scoped token only after policy approval. This reduces the chance that secrets appear in prompts, logs, or generated output.
Use approval according to risk
Not every call needs a person. Reading public documentation may proceed automatically; accessing internal data needs scope checks; bulk messaging, production changes, or financial operations require step-up authentication and explicit approval. Policy should reflect potential impact, reversibility, and confidence in the available context.
Auditability and explanation
Record the principal, policy version, tool, sanitized parameters, target resource, decision, approver, result, and correlation ID. Do not store raw secrets or unnecessary sensitive data. Logs should reconstruct an action chain without becoming another source of exposure.
Implementation checklist
- Inventory tools and classify operations as read, write, or destructive.
- Derive agent authority from the user's existing rights; do not create implicit new permissions.
- Keep policy enforcement outside the model and outside prompt content that can be manipulated.
- Use short-lived credentials bound to audience, scope, and time.
- Require approval for high-impact actions and show exactly what the agent will do.
- Test prompt injection, confused-deputy, replay, and multi-tool scope escalation.
A sound design does not try to determine whether an agent has good intentions. It assumes every proposed action must pass an auditable policy check before reaching a real system.
Why developers should care
AI agents can execute multi-step plans at machine speed. If authorization is checked only at sign-in, a bad instruction or abused tool can turn legitimate access into actions that exceed the user's intent.
Recommended action
- 1Inventory every agent tool, classify operations by impact, and place a mandatory policy enforcement point before any call that reads internal data or changes system state.