Quick summary
- Google Project Zero has examined a bypass of Administrator Protection, a Windows 11 25H2 feature intended to replace UAC with more controlled elevation. The finding makes privilege boundaries, workstation hardening, and least-privilege testing immediate concerns for engineering teams.
- A weakness in local administrator elevation can expose developer workstations, credentials, source code, signing material, and connected software-delivery systems.
- Inventory Windows 11 25H2 endpoints and administrator-dependent workflows, evaluate the feature in an isolated test group, and monitor authoritative remediation guidance before broad deployment.
What happened
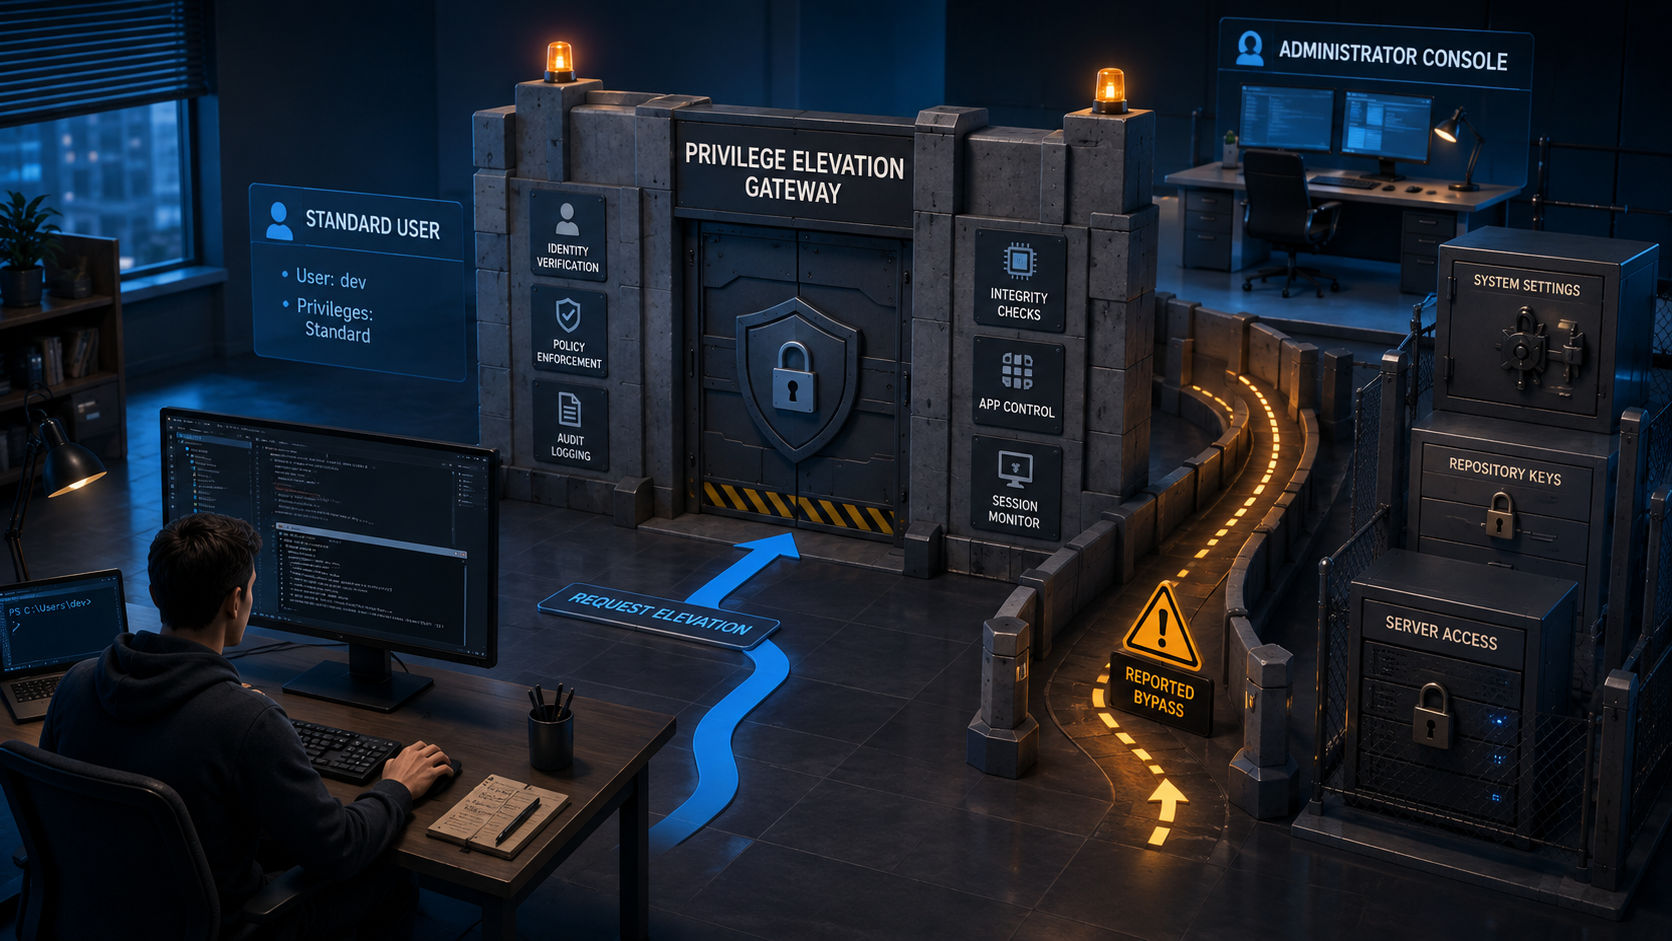
Windows 11 25H2 introduces Administrator Protection with an ambitious goal: replace User Account Control (UAC) with a more robust mechanism that gives a local user administrator privileges only when required. A Google Project Zero analysis titled “Bypassing Windows Administrator Protection” indicates that this new elevation path can still be circumvented.
The supplied record does not establish the bypass prerequisites, affected configurations, exploitation impact, or remediation status. The responsible takeaway is therefore narrower than “Administrator Protection is broken”: teams should treat elevation as a security boundary that requires layered controls and independent testing, not merely as a confirmation prompt.
What is Administrator Protection designed to change?
According to Project Zero’s description, the feature is meant to let a local user access administrator privileges only when necessary. That is a just-in-time privilege objective: ordinary work remains less privileged, while a specific administrative operation receives elevated authority.
This distinction matters on developer workstations. Package managers, installers, debuggers, build tools, local services, and automation scripts can all encounter operations that request system-level access. Keeping an entire interactive session elevated gives any compromised process in that session a potentially broader scope than the task requires.
The security value of just-in-time elevation depends on more than when a dialog appears. A robust design must preserve the association among the requesting identity, initiating process, intended operation, elevated process, and resulting access. The supplied material does not explain how 25H2 implements those relationships, so implementation-specific claims would be premature.
What does a bypass mean—and what does it not prove?
The Project Zero title supports the existence of a way around the protection, but the available evidence here is insufficient to describe or reproduce it. It does not, by itself, demonstrate remote compromise, universal exposure across all Windows 11 systems, or an attack that works without an initial foothold.
The broader lesson is the difference between a consent experience and an authorization boundary. A visible prompt can help a person notice a sensitive action. Security still depends on whether the operating system grants authority to the correct process, limits that authority to the intended resources, and prevents less-trusted code from influencing the privileged operation.
Privilege elevation also sits inside a wider identity lifecycle. As discussed in the shift toward continuous identity governance and behavioral detection, a single approval cannot substitute for observing what an identity and its processes do after access is granted.
How should developer and platform teams respond?
Start by identifying where local administrator rights appear in engineering workflows. Each occurrence should have an owner and a concrete reason; installing a system component is different from routinely running an editor, terminal, browser, build, or test suite with elevated rights.
- Run IDEs, shells, browsers, source-control clients, and build agents as standard users wherever practical.
- Separate machine-level installation from routine dependency resolution, compilation, and testing.
- Restrict repository tokens, signing keys, cloud credentials, and other secrets to the processes that require them.
- Collect available telemetry for privileged process creation and sensitive configuration changes.
- Test internal applications under non-administrator accounts to expose hidden privilege dependencies.
These steps are not a vendor patch and should not be presented as one. They reduce the potential blast radius of a compromised local process and make anomalous elevation easier to investigate while the technical status of the reported bypass is clarified.
Teams should also avoid building product logic that treats “the user is a local administrator” as sufficient authorization. Applications should validate access at the operation and resource level, particularly for update services, plugins, local agents, and other components that bridge user and system contexts.
What should organizations validate before broad adoption?
Administrators need authoritative guidance on affected builds, required preconditions, mitigations, and update status. None of those details is confirmed in the supplied crawl record, nor does it say whether Administrator Protection is enabled by default for a given installation or policy configuration.
A controlled evaluation can still be useful. Build a test matrix covering standard users, local administrators, representative application types, and approved elevation workflows. Verify that each task obtains only its expected permissions, that elevated authority does not persist unexpectedly, and that audit data identifies the relevant identity and process chain.
Do not run unverified exploit material on production workstations. Inventory Windows 11 25H2 systems, preserve relevant security telemetry, test policy changes in an isolated environment, and keep a rollback path for configurations that disrupt necessary engineering work.
The reporting also offers a useful procurement question for any privilege-management product: what exactly forms the enforcement boundary? A defensible answer should cover process isolation, identity binding, lifetime, resource scope, observability, and failure behavior—not only the appearance of an approval screen.
Conclusion
- Administrator Protection aims to provide administrator privileges only when a local task needs them.
- Project Zero’s bypass finding means teams should not assume the new mechanism is an absolute boundary.
- The supplied evidence does not confirm exploit conditions, affected configurations, or remediation.
- Least-privilege workflows, isolated testing, and elevation telemetry remain practical defenses.
Related reading
- Identity security shifts to continuous governance and behavioral detection
- AI agent security must extend beyond the model boundary
- AI agents move from security assistance to active testing and response
Source
Why developers should care
A weakness in local administrator elevation can expose developer workstations, credentials, source code, signing material, and connected software-delivery systems.
Recommended action
- 1Inventory Windows 11 25H2 endpoints and administrator-dependent workflows, evaluate the feature in an isolated test group, and monitor authoritative remediation guidance before broad deployment.