IMPORTANTA high-impact development that should be prioritized for monitoring.Security
Supply-chain security must cover dependencies and developer tools
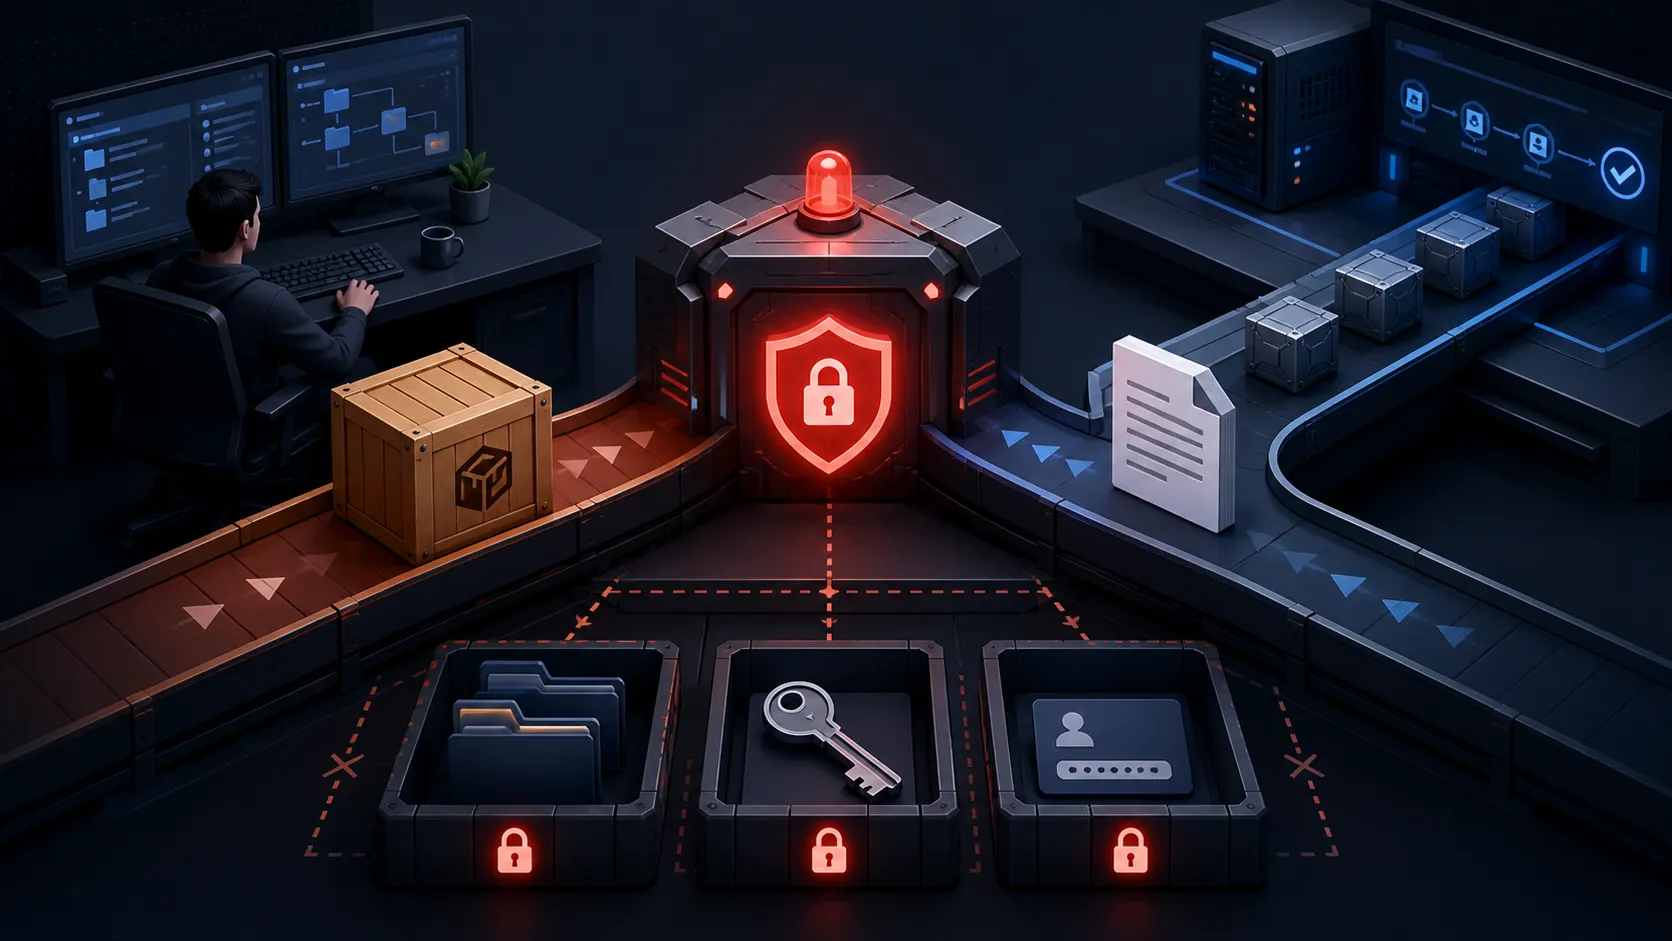
Reports involving malicious Rust crates and exploitable VS Code extension behavior show that supply-chain risk extends beyond production dependencies. Editors, build systems, and plugin ecosystems belong in the same security model as application packages.