Quick summary
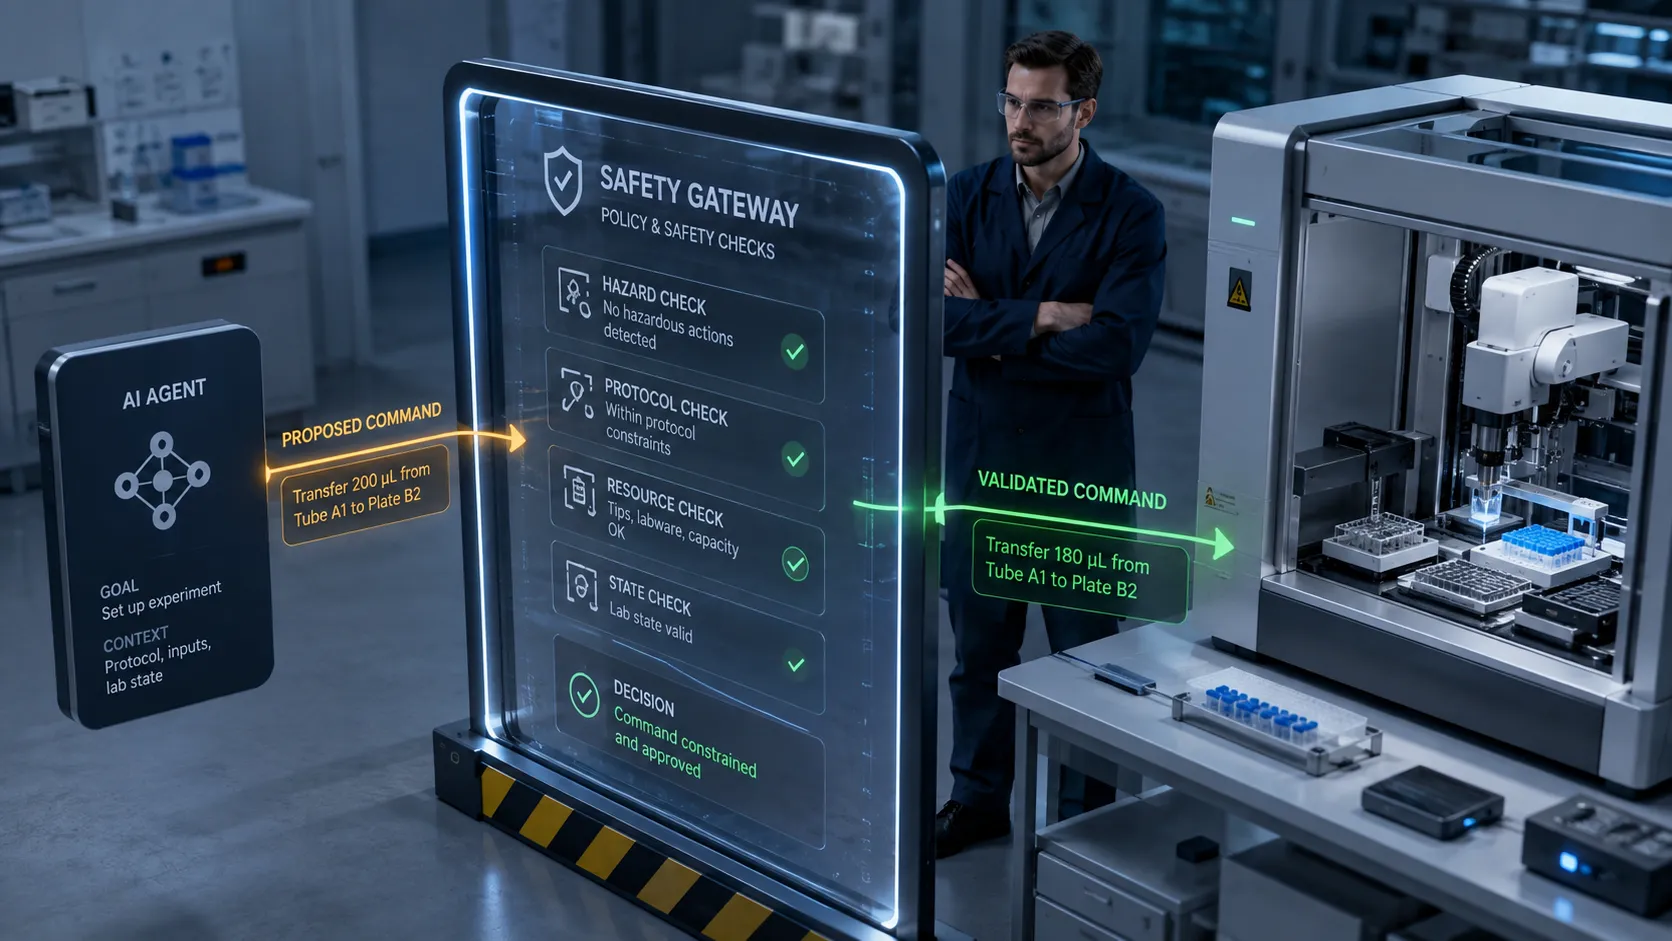
- AI integrations in Messages and desktop apps can make assistance more contextual, but they also expand access to sensitive data and actions. Teams should hold back broad automation until consent, review, revocation, and recovery are concrete product capabilities.
- User trust will depend on how clearly a product limits and explains AI access, not merely on how useful its output appears.
- Before granting AI read, write, or send access, build a task-level capability matrix and ship preview, confirmation, revocation, and action-history paths.
What happened
The closer an AI assistant gets to personal data, the more useful it may become—and the more carefully it must be controlled. Messages, app content, and calendars can contain relationships, work material, routines, and other sensitive context.
ChatGPT's Apple Messages plug-in and Meta AI's Mac app, which is positioned around talking to apps, make the shared design question sharper: what can the assistant see, do, and retain access to?
Access should not be an all-or-nothing switch
A general permission for messages or apps may be far broader than the immediate job requires. Ask for the smallest useful scope: a selected conversation, one draft operation, or one specified action.
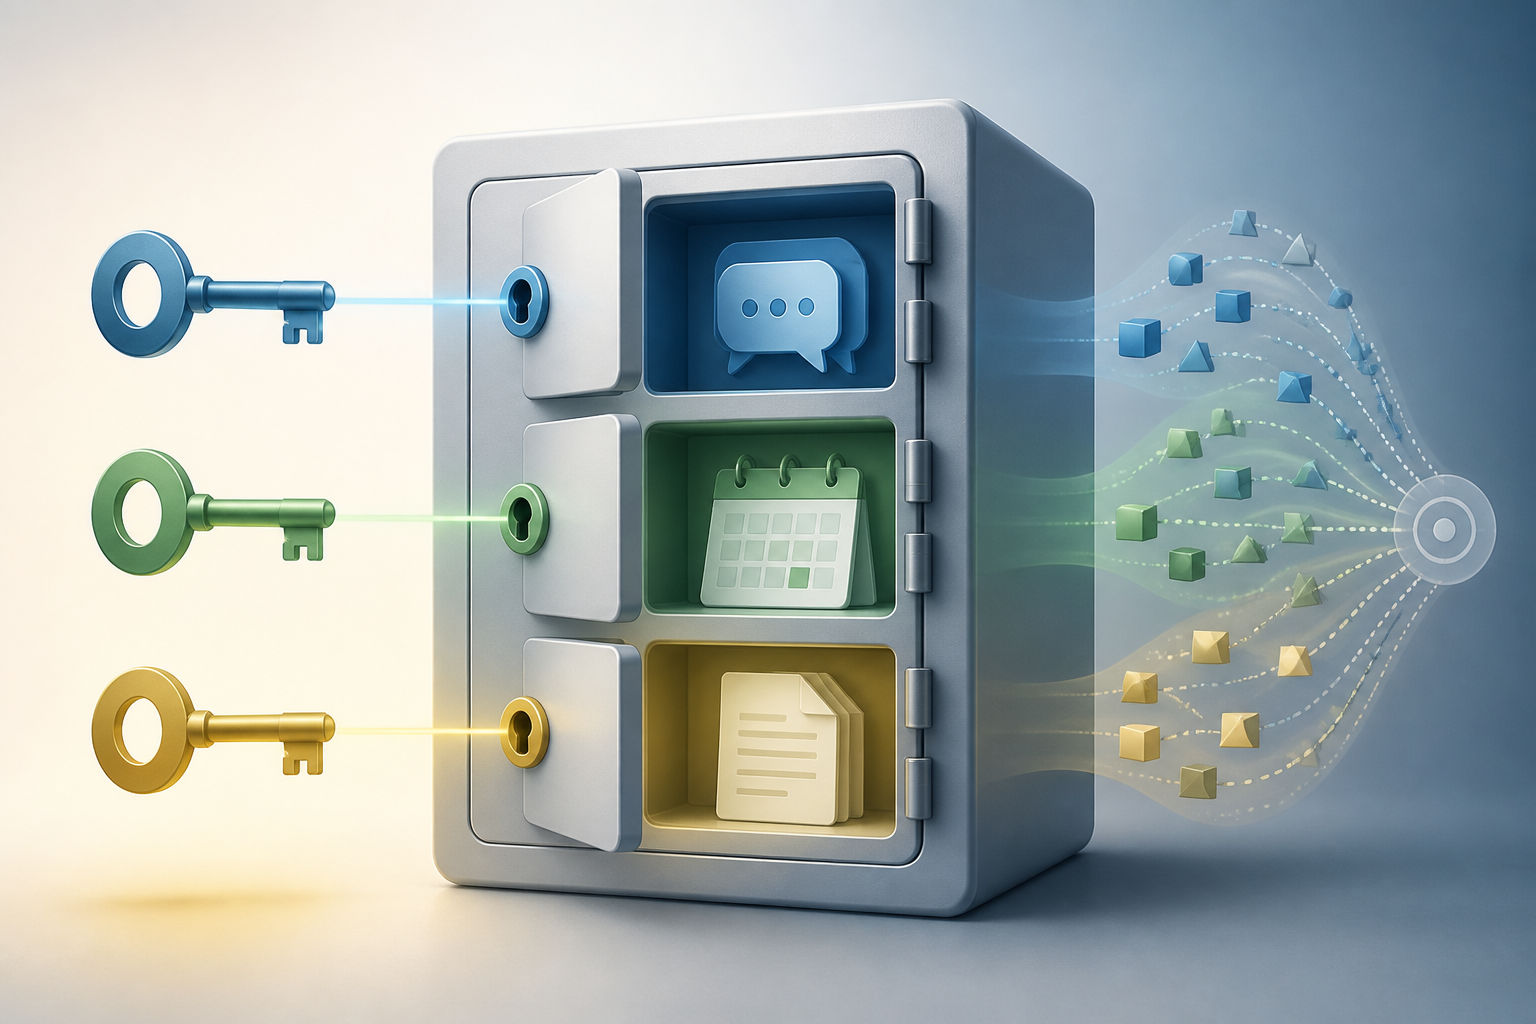
Permissions should also expire when that matches the task. People can assess a request more easily when it is tied to a recognizable goal and duration than when it grants an open-ended capability for unspecified future use.
Meaningful consent needs inspectability
People cannot make an informed decision if they do not know which material will be used or where the result will go. Before a send, share, or modification, show the target, preview, and cancellation path.
- Show the data included in a task, not only a permission label.
- Present a draft or intended change before committing it.
- Record AI-initiated actions somewhere users can find them.
- Make it understandable to revoke access or remove a connection.
Risk is more than data exposure
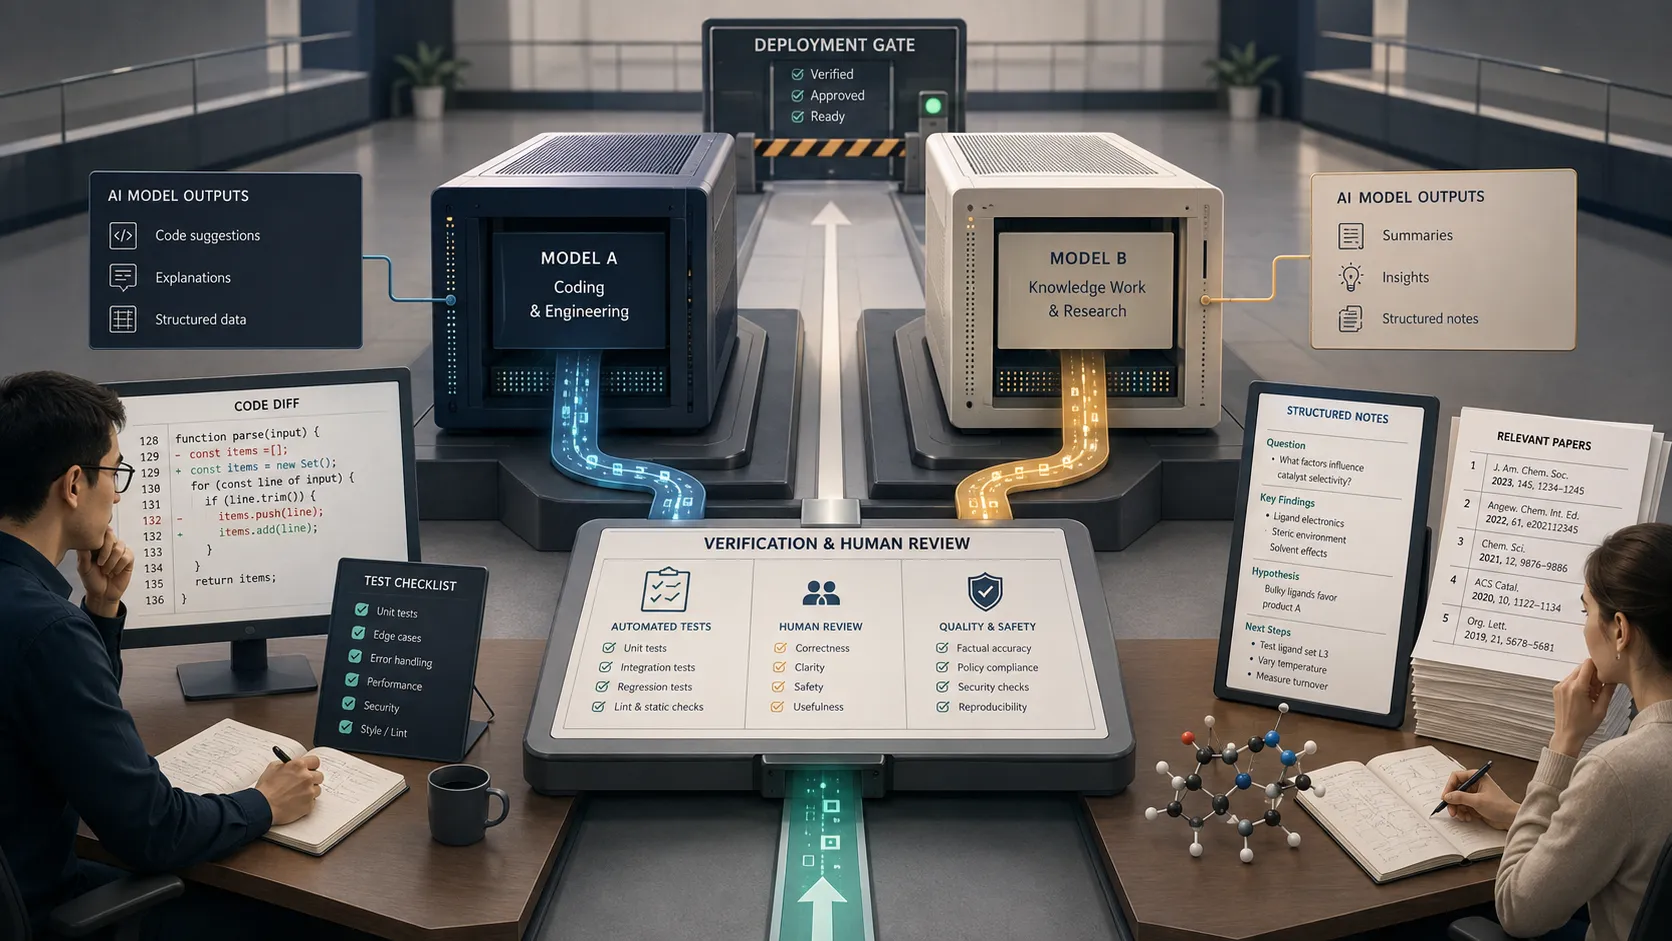
A system can remain within its data scope and still cause harm by inferring the wrong intention or acting at the wrong time. Safety therefore includes output controls: refusal boundaries, confirmation for consequential calls, and a way to report mistakes.
That is also why not every integration should become fully autonomous. A draft may be the correct product form instead of an auto-sending agent, especially when context shifts quickly or the cost of error is high.
Prepare the product before expanding authority
Build a capability matrix for each tool: data read, allowed change, confirmation point, and reversal path. Then test misunderstanding, missing context, and changed-user-mind cases—not just successful demonstrations.
In an early release, keep write and send capabilities confirmation-gated. Consider narrow automation only after evidence shows that people understand the behavior, can verify outcomes, and can recover from a bad result.
In 5 Minutes
- AI access to messages and apps increases exposure to sensitive data and actions.
- Permissions should be minimal, task-specific, and time-bounded when possible.
- Trustworthy consent requires visible inputs, intended outcomes, and cancellation.
- Hold broad automation until review and recovery are robust.
Sources
- ChatGPT can now send texts for you with new Apple Messages plug-in
- Linkdaze’s smart calendar is built to run a household, not just track a schedule
- Meta brings Pocket, an app that lets you vibe-code and share games, to US users
- Meta AI’s new Mac app wants you to talk to your apps
- Google packs Search and Gemini with new AI study tools
- Amazon makes its AI-powered Alexa+ free on Fire TV, no Prime required
- Calendly throws its hat into meeting note-taker circus
- Why Apple’s camera-equipped AirPods may not be the ‘pervert pods’ consumers fear
Why developers should care
User trust will depend on how clearly a product limits and explains AI access, not merely on how useful its output appears.
Recommended action
- 1Before granting AI read, write, or send access, build a task-level capability matrix and ship preview, confirmation, revocation, and action-history paths.