Quick summary
- As MCP reaches real use, defining a tool is only the starting point. A server needs a clear contract, authorization boundaries, operational behavior, and accountable ownership.
- A useful tool without reliable operations becomes a weak point for both the agent and the systems behind it.
- Choose one low-risk MCP tool and write a one-page operating contract covering owner, permissions, logs, tests, and rollback.
What happened
An MCP tool can be created quickly. Once an agent uses it to read data or change state, however, the server should be treated as an integrated service.
The focus of building, securing, and serving MCP servers in practice signals a shift beyond “how do I define a tool?” The more valuable question is whether a server can be used, observed, and changed safely.
Keep the tool contract narrow and explicit
Design each tool around a task that is understandable and verifiable. Ambiguous inputs or overly broad actions make correct agent use harder and policy enforcement less precise.
Before release, specify accepted input, expected results, side effects, and possible errors. That does not prove every model will behave perfectly; it reduces ambiguity in the interface.
Authorize actions, not intentions
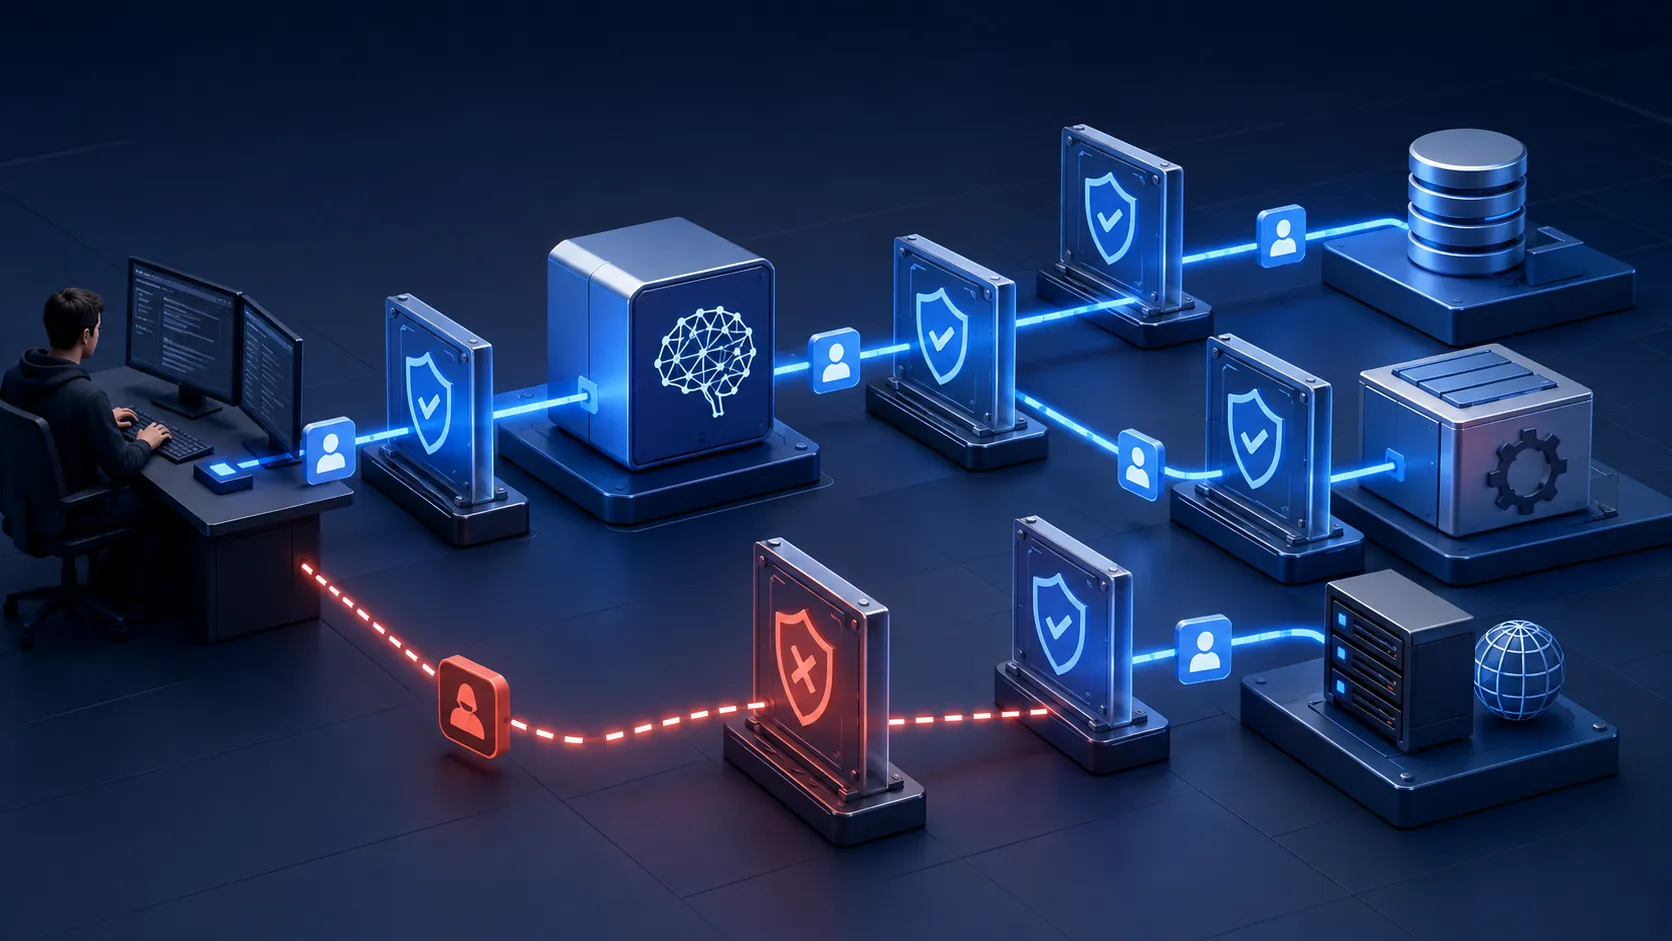
Do not rely on an agent instruction to prevent risky work. The server must enforce authorization and limits at the point where the action occurs.
- Separate read operations from operations with side effects.
- Constrain resource scope instead of granting global access.
- Use confirmation or an additional workflow for sensitive actions where appropriate.
- Log for traceability without collecting unnecessary data.
Operations are a functional requirement
Every server needs an owner, a release process, and a diagnostic path. This matters especially when failure appears at the transport boundary: the discussion of stdio traps that leave an MCP server unresponsive is a reminder that “works on my machine” is not a deployment standard.
Test startup behavior, error visibility, and rollback of changes. These practices may be simple for a first server but become expensive to retrofit once multiple clients depend on it.
Set a threshold before scaling
Trial one low-risk tool with a small user group and explicit stop criteria. Expand only after you have signals about failures, permissions, and actual use.
In 5 Minutes
- An MCP server should be operated as an integrated service.
- Narrow, explicit tool contracts reduce ambiguity.
- Authorization belongs at the action point.
- Ownership, diagnostics, and rollback should precede scale.
Sources
Why developers should care
A useful tool without reliable operations becomes a weak point for both the agent and the systems behind it.
Recommended action
- 1Choose one low-risk MCP tool and write a one-page operating contract covering owner, permissions, logs, tests, and rollback.