Quick summary
- Wiz argues that AI changes the context around data risk: organizations need to understand what data is connected, exposed, and why. That understanding is a prerequisite for trustworthy agents, response, and remediation.
- An agent with broad access can amplify pre-existing problems in data classification, exposure, and entitlements.
- Build an agent data-source inventory that records ownership, sensitivity, exposure, and access model.
What happened
AI does not create every data risk from scratch, but it can make existing access paths easier to exploit. As agents combine data from multiple sources, security must ask what is connected, how it is exposed, and in what context.
Wiz argues that AI changes the context around data risk, making an understanding of connection, exposure, and cause critical.
Agent access is a data problem
An agent is not merely a new interface. It creates a new retrieval route across data stores, documents, and SaaS. Where classification, entitlements, or ownership are unclear, the agent can expose that weakness at greater scale.
Do not grant access on the assumption that an agent will only answer harmless questions. Identify sensitive data, allowed sources, and the users the agent may represent.
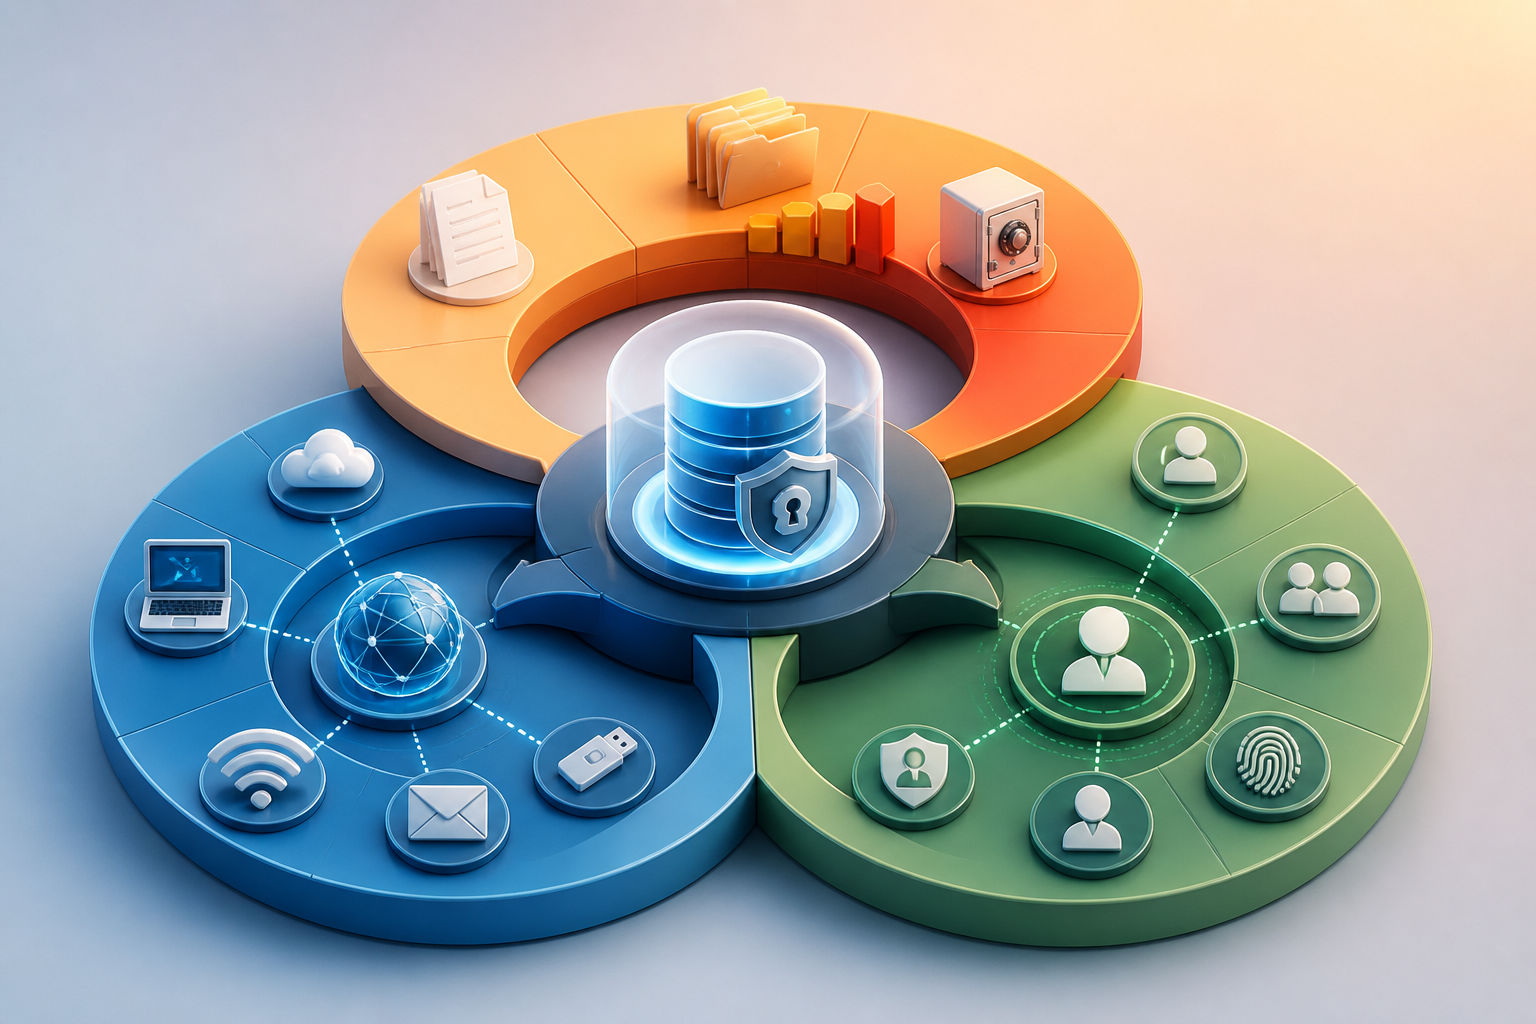
Reconnect three layers of context
- Data: its type, owner, and sensitivity.
- Exposure: where it can be accessed or shared.
- Identity: the user, workload, or agent requesting it.
Together, these layers let security teams assess actual risk rather than isolated configurations or assets.
Set guardrails before expanding agent access
Use data-source inventory and access posture as rollout criteria. A source without an owner, clear policy, or bounded permissions should remain outside automated retrieval until it is addressed.
This is also a prerequisite for safe remediation: automation cannot reliably correct a problem without understanding its effect on data and access paths.
In 5 Minutes
- AI can amplify existing data risk through new retrieval paths.
- Connection, exposure, and cause are foundational security context.
- Link data, exposure, and identity information.
- Expand agents only to sources with clear ownership and policy.
Sources
- Propagate user authorization context in AI agents with Amazon Bedrock AgentCore
- Implement custom authentication for tools integration using request Lambda interceptor in AgentCore Gateway
- Wiz Red Agent Finds Its Way Into Snowflake’s Internal Jira Through a Flaw in a GitHub Copilot–Assisted PR
- The Closed Loop Remediation Playbook with Wiz
- Securing Data in the AI era
- Wiz at Black Hat 2026: Driving AI Threat Readiness
- Introducing the Wiz Sensor for Developer Workstations to Protect Endpoints in the AI Era
Why developers should care
An agent with broad access can amplify pre-existing problems in data classification, exposure, and entitlements.
Recommended action
- 1Build an agent data-source inventory that records ownership, sensitivity, exposure, and access model.